
cybersecurity

PREDICTIVE THREAT DETECTION and AUTOMATED RESPONSE
cybersecurity

Digital Armor: Defending Against Cyber Threats

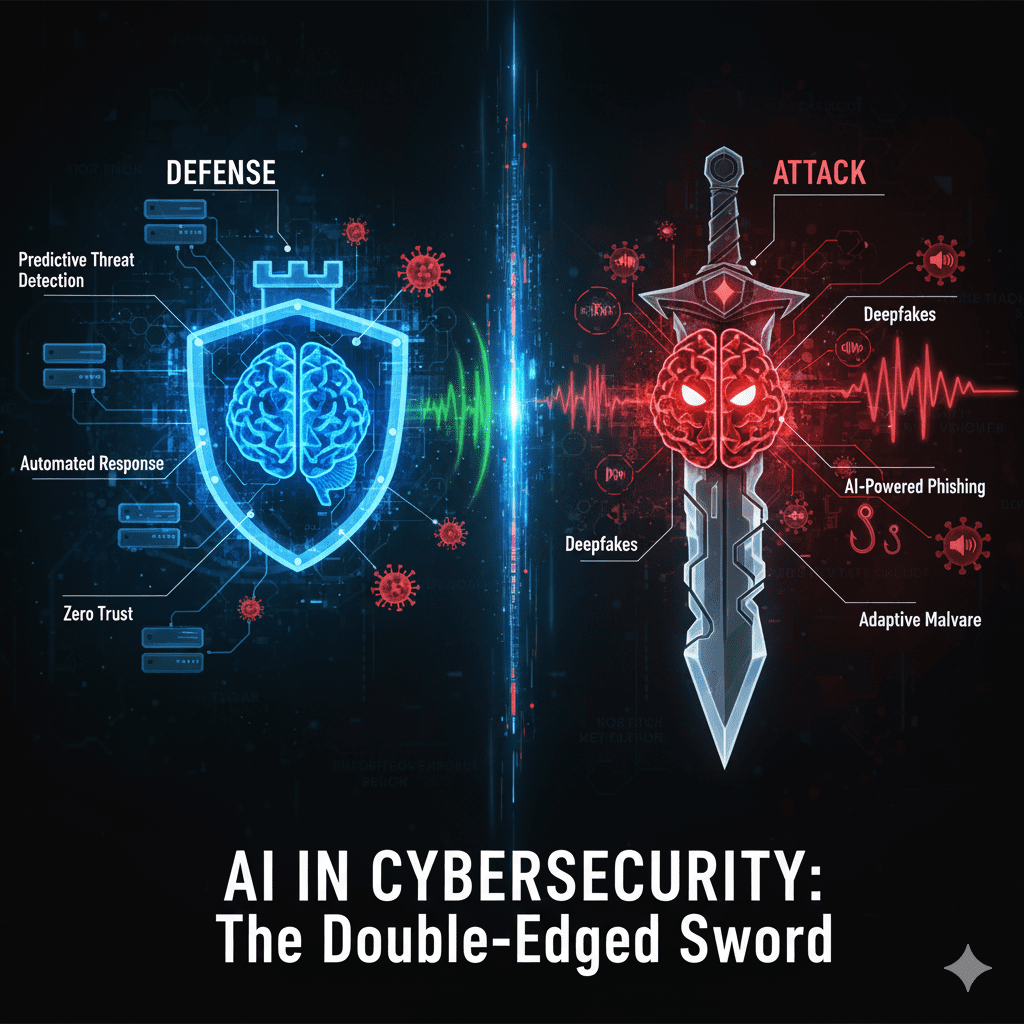
Introduction For decades, the world of cybersecurity has been a high-stakes cat-and-mouse game. Security professionals build a wall, and hackers find a way over it. But today, this game is being fundamentally transformed by a powerful new player: Artificial Intelligence. AI is not just another tool; it’s a revolutionary force acting as both the strongest shield and the most dangerous new weapon. This article explores the dual role of AI in Cybersecurity, breaking down how it’s creating unprecedented defenses while simultaneously arming attackers with terrifying new capabilities The New Shield: AI as a Defensive Powerhouse The primary advantage of AI in a defensive role is its ability to process and analyze data at a scale and speed no human team could ever hope to match. While a human analyst sleeps, an AI security model is monitoring billions of events, looking for the one tiny anomaly that signals an attack. 1. Predictive Threat Detection Before AI, most security systems were reactive. They relied on “signatures”—the digital fingerprints of known malware. This meant a virus had to successfully attack someone first before it could be identified and blocked. AI, specifically machine learning, is predictive. It learns the normal, baseline behavior of your network, your users, and your devices. It can then spot suspicious deviations before a full-blown breach occurs. This includes: Behavioral Analysis: Is a user account that normally works from 9-to-5 suddenly trying to access sensitive files at 3:00 AM from a different country? AI flags this instantly. Anomaly Detection: Does a “smart” device like a thermostat suddenly start trying to communicate with an unknown server? AI can see this as a potential IoT (Internet of Things) attack. Pattern Recognition: AI can analyze global threat feeds and identify new attack patterns as they emerge, proactively blocking them before they even reach your network. 2. Automated Incident Response In a cyberattack, every second counts. A ransomware attack can encrypt an entire company’s files in minutes. AI doesn’t need to wait for approval; it can act in milliseconds. This is known as SOAR (Security Orchestration, Automation, and Response). Here’s a typical automated response scenario: Detect: An AI-powered sensor identifies a new, unknown program exhibiting ransomware-like behavior (e.g., rapidly encrypting files) on an employee’s laptop. Isolate: The AI immediately executes a predefined rule: it automatically disconnects that specific laptop from the company network, containing the threat. Investigate: The AI gathers all relevant data—what the program was, where it came from, what files it touched—and creates a report. Alert: It then sends an alert to a human security analyst, presenting the report and the action it took. The threat is neutralized before it could spread. The Future: An AI vs. AI Battleground This leads to an inevitable future: the front line of AI in Cybersecurity will be an AI-versus-AI battle. It will be a silent, high-speed war fought in milliseconds, with defensive AI models trying to detect and stop offensive AI-driven attacks. In this new era, the old security model of “trust but verify” is dead. The new model, which AI is perfect for, is Zero Trust. Zero Trust Architecture means you trust nothing and no one by default. It doesn’t matter if a login request comes from inside the office or outside; it must be verified. AI helps enforce this by continuously analyzing behavior. Just because you entered the right password doesn’t mean you are who you say you are. If your “logged-in” account suddenly starts acting suspiciously, the AI can force you to re-authenticate or block your access. Conclusion AI in Cybersecurity is a revolutionary, double-edged sword. It offers our most powerful hope for a secure digital future, capable of analyzing threats and responding at superhuman speeds. At the same time, it arms our adversaries with tools to create highly deceptive scams and intelligent malware. The key takeaway is that we can’t ignore it. For businesses, investing in modern, AI-powered defensive tools is no longer an option—it’s a necessity for survival. For individuals, it requires a new level of vigilance. In this new world, adaptability is everything. The future of security will be defined by who has the smarter, faster, and more adaptable AI. FAQ Q1: What is AI in Cybersecurity? AI in Cybersecurity refers to the use of artificial intelligence and machine learning to detect, predict, prevent, and respond to cyber threats. It moves beyond traditional, rule-based security by learning from data to identify new and unknown threats based on behavioral anomalies. Q2: Can AI replace human cybersecurity professionals? No, AI is a tool to augment human professionals, not replace them. AI can handle the massive, high-speed data analysis, but it still lacks human intuition, creativity, and strategic decision-making. AI flags the problem and contains it; the human analyst investigates the “why” and “how” to build a stronger long-term strategy. Q3: What is the biggest threat from AI in cyberattacks? Currently, the most accessible and dangerous threat is AI-powered social engineering, including deepfake audio and video. These attacks target the weakest link in any security system—human psychology—and are incredibly difficult to defend against with technology alone. Q4: How can a small business afford AI-powered security? While developing a custom AI model is expensive, most AI-powered security is now sold “as-a-service.” Many modern antivirus, firewall, and email security providers (like Microsoft, Google, and CrowdStrike) have already integrated AI and machine learning into their standard products, making it accessible and affordable for businesses of all sizes.
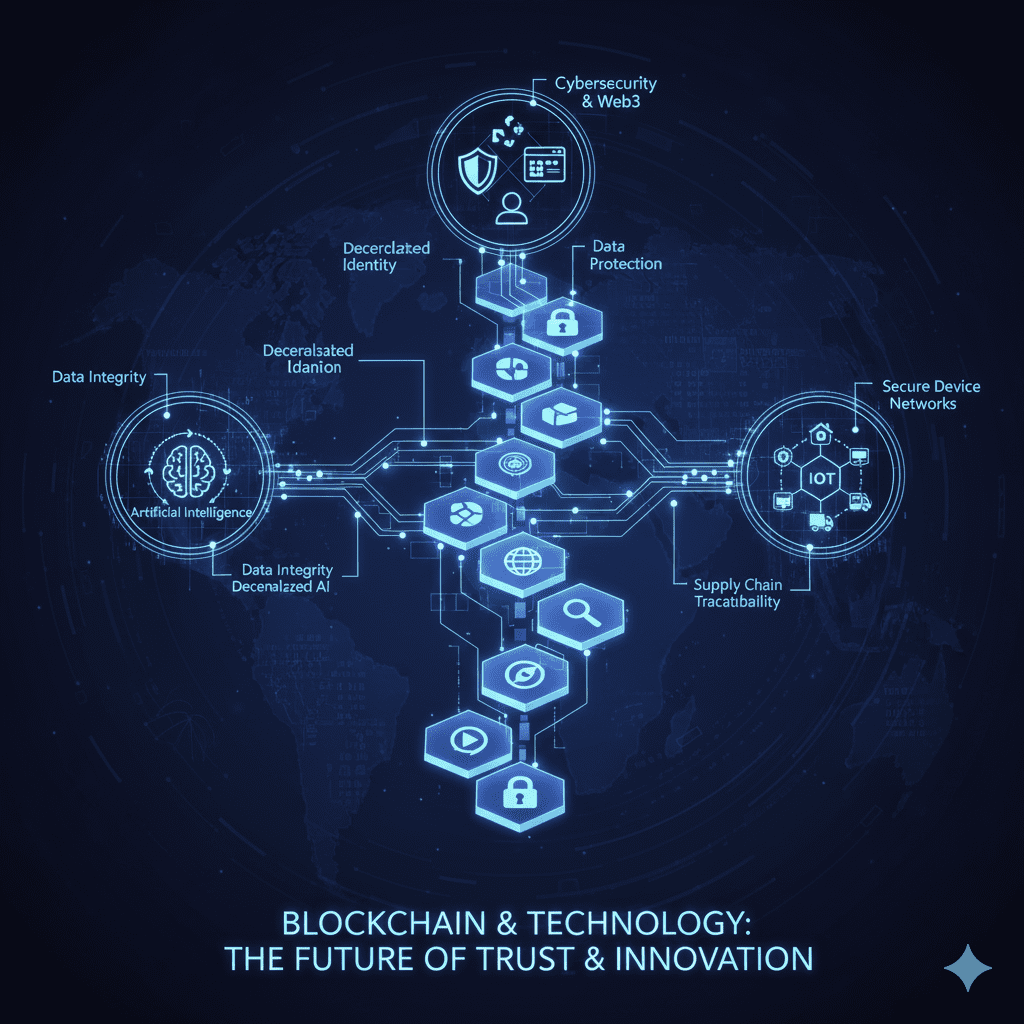
A futuristic infographic titled 'BLOCKCHAIN & TECHNOLOGY,' showing a central blockchain icon connected to other technologies like AI, IoT, Cybersecurity, DeFi, NFTs, and Web3.
Blockchain & Technology

Blockchain’s Role in Building Tomorrow’s Tech

Introduction What do AI, cybersecurity, and the future of the internet (Web3) have in common? They all have critical problems with trust, security, and centralization. Blockchain technology is emerging as the key solution to all three. It’s the invisible architecture that provides the security for our data, the transparency for our transactions, and the ownership of our digital assets. Let’s dive into the technology ecosystem that blockchain is building right now. What is Blockchain? At its simplest, a blockchain is a secure, digital ledger that is shared among many computers in a network. Once a piece of information (a “block”) is added to the ledger, it is linked to the previous block using cryptography, creating a “chain.” This structure makes it immutable, meaning once data is recorded, it is extremely difficult to change or remove. Core Components Decentralization: Instead of one person or company controlling the ledger (like a single bank), the ledger is copied and spread across many computers. This means no single entity has control, and there is no single point of failure. Cryptography: Every transaction is secured and verified using advanced math. This ensures that only the rightful owner can access their assets and that all records are authentic. Blocks: These are the “pages” of the ledger. Each block contains a batch of recent, verified transactions. Consensus Mechanism: This is the “rulebook” that the network follows to agree on which transactions are valid and can be added to the chain (e.g., Proof-of-Work or Proof-of-Stake). The Big Trends: Web3, DeFi, and NFTs Blockchain is the foundational technology for several major trends: Web3: This is the idea of a new, decentralized internet. Web1 was the “read-only” internet (static websites). Web2 is the “read-write” internet we use today (social media, user-generated content), but it’s controlled by large tech companies. Web3 aims to be a “read-write-own” internet, where users control their own data and identity using blockchain. DeFi (Decentralized Finance): This is an entire ecosystem of financial applications built on blockchain. It aims to recreate traditional financial systems (like lending, borrowing, and trading) without the need for intermediaries like banks. Users interact directly with smart contracts. NFTs (Non-Fungible Tokens): An NFT is a unique digital certificate of ownership for an asset (like a piece of digital art, a collectible, or even a real-world item). “Non-fungible” means it’s one-of-a-kind and cannot be replaced by another, unlike a dollar bill, which is fungible. This ownership is recorded and verifiable on the blockchain. Blockchain’s Integration with Other Technologies Blockchain doesn’t exist in a bubble. Its real power is unlocked when combined with other technologies. 1. Artificial Intelligence (AI) Data Integrity: AI models are only as good as the data they’re trained on. Blockchain can provide an immutable, verifiable audit trail for AI training data, ensuring it hasn’t been tampered with and proving its origin. Decentralized AI: It enables “Federated Learning,” where an AI model can be trained across multiple devices without the users’ private data ever leaving their device. The blockchain is used to log and verify the model’s updates, protecting user privacy. 2. Internet of Things (IoT) Security: IoT networks often have thousands of simple devices (like sensors) that are vulnerable to hacking. Blockchain can create a secure, decentralized network for these devices to communicate directly and verifiably, preventing a central server from being hacked. Traceability: For supply chains, an IoT sensor can log a package’s temperature and location to a blockchain at every step. This creates a tamper-proof record that all parties (the producer, the shipper, the customer) can trust. 3. Cybersecurity Decentralized Identity: Instead of relying on Google or Facebook to log in to websites, blockchain allows for Self-Sovereign Identity (SSI). You would control your own digital identity, stored securely, and grant specific, temporary access to services that need to verify it. Mitigating Attacks: By decentralizing data storage, blockchain can help prevent large-scale data breaches. It also makes systems more resilient to Distributed Denial of Service (DDoS) attacks, as there is no single central server to overwhelm Conclusion In conclusion, blockchain has evolved far beyond its origins in cryptocurrency. It is now the essential “trust layer” for the next generation of technology. By providing a decentralized, immutable, and transparent ledger, it solves the critical vulnerabilities in our current systems. It’s the thread that securely connects AI models to verifiable data, enables IoT devices to communicate without a central point of failure, and provides the very foundation for a user-owned internet in Web3, DeFi, and NFTs. As we move forward, it’s clear that blockchain isn’t just another technology in the stack; it’s the fundamental architecture the future is being built on. FAQ Q1: What is blockchain in the simplest terms? Blockchain is a digital ledger, like a shared notebook, that is duplicated and spread across many computers. Once a transaction (a “block”) is added to this notebook, it’s cryptographically linked to the one before it, creating a “chain.” This structure makes the data immutable, meaning it’s nearly impossible to change or tamper with. Q2: Isn’t blockchain just for Bitcoin and cryptocurrency? No. While Bitcoin was the first major application, it’s just one use case. Blockchain is the underlying technology that enables cryptocurrencies, but its core value is in providing a secure and decentralized way to record any kind of data. It’s now being used in supply chains, healthcare, voting systems, cybersecurity, and more. Q3: What’s the difference between Blockchain and Web3? Think of blockchain as the tool and Web3 as the movement. Blockchain is the specific technology (a decentralized ledger). Web3 is the broader vision for a new, decentralized internet built using tools like blockchain, crypto, and decentralized networks. Web3’s goal is to shift control from large tech companies to individual users. Q4: How does blockchain work with Artificial Intelligence (AI)? Blockchain can be seen as the “source of truth” for AI. Data Integrity: It provides a tamper-proof log of the data used to train an AI model, so you can verify its origin and quality. Privacy: It enables federated learning,

Futuristic SIEM dashboard interface overlayed with application security icons and the Australian flag, representing application security solutions for Australia
Artificial Intelligence

SIEM for App Security in Australia

Introduction Organisations in Australia are grappling with a rapidly evolving cyber threat landscape where application-layer attacks are more frequent and far-reaching than ever before. As digital infrastructures grow more complex and interconnected, security teams need efficient solutions to detect, investigate, and respond to threats targeting their applications. Security Information and Event Management (SIEM) platforms have emerged as a vital line of defense, providing both real-time visibility and advanced analytics to help businesses stay ahead of attackers. This blog explores why SIEM has become indispensable for Australian organisations seeking robust application security—and how it serves as a strategic weapon against the next generation of threats.​ SIEM for App Security in Australia How SIEM Protects Modern Applications Centralised Log Management: SIEM consolidates logs from across your entire stack—web apps, APIs, databases, and cloud services—transforming fragmented data into one coherent intelligence stream.​ Real-Time Threat Detection: Automated monitoring and correlation engines analyse events at scale, detecting suspicious behaviours and potential breaches before they escalate.​ Incident Response Enablement: SIEM alerts analysts to actionable threats, allowing them to prioritise and respond quickly, preventing damage and downtime.​ Compliance Support: With Australia’s data privacy regulations and the Security of Critical Infrastructure Act, SIEM helps organisations maintain auditable records and meet regulatory requirements efficiently.​ Key Benefits Early Breach Identification: By connecting seemingly minor events, SIEM unmasks coordinated attacks—like credential-stuffing or API abuse—that could remain undetected in siloed systems.​ Streamlined Security Operations: Automating event triage and investigation reduces the manual workload for security professionals and accelerates incident remediation.​ Integration with SOAR: Many SIEM platforms now work alongside Security Orchestration, Automation, and Response (SOAR) tools, further improving response times and consistency.​ SIEM in the Australian Security Landscape Australian businesses face increasingly complex and sophisticated attacks, prompting widespread adoption of SIEM solutions. According to recent market analysis:​ Growth Driven by Compliance and Threats: Demand for SIEM is surging as organisations strive to comply with the Australia Cyber Security Strategy and protect critical infrastructure, especially in sectors like BFSI, IT, and government.​ Rise of AI and Automation: Modern SIEM systems leverage artificial intelligence and machine learning to detect threats and automate responses, addressing the skills shortage and increasing detection accuracy.​ Operational Challenges: Integrating SIEM with legacy infrastructures, managing the volume of security data, and controlling costs remain significant hurdles for Australian businesses.​ Use Cases & Statistics Essential Eight Maturity: SIEM is a cornerstone for achieving the Australian Signals Directorate’s Essential Eight maturity model, translating to better preparedness and faster detection.​ Incident Response Uptake: 86% of Australian entities had an active incident response plan in 2024, showing a maturing industry that sees SIEM as critical to readiness.​ Market Outlook: The SIEM market in Australia is set for robust growth, fueled by both enterprise and SME adoption, as real-time detection and actionable security analytics become business imperatives.​ Conclusion SIEM has become a non-negotiable pillar for application security in Australia’s cyber threat environment. By centralising log data, delivering advanced analytics, and supporting compliance, SIEM empowers organisations to defend against evolving threats efficiently and confidently. Investing in SIEM today means not just meeting regulatory demands, but enabling your team to spot sophisticated attacks much earlier—and respond faster. As cyber risks grow, the question is not if, but how soon your organisation will face them. Make SIEM the cornerstone of your cyber strategy and stay a step ahead. Ready to take your application security to the next level? Explore advanced SIEM platforms or consult with a cybersecurity expert to start protecting your business today! FAQ 1. What is SIEM and why is it important for Australian businesses? SIEM stands for Security Information and Event Management—a platform to collect, analyse, and correlate security data in real-time, crucial for early threat detection and regulatory compliance.​ 2. How does SIEM help meet Australian compliance standards? SIEM provides auditable logs, automated reporting, and breach detection, helping organisations comply with regulations like the Privacy Act and Security of Critical Infrastructure Act.​ 3. What kinds of threats can SIEM detect in applications? SIEM detects credential stuffing, API abuse, insider threats, and targeted cyber-attacks by correlating anomalous events across application layers.​ 4. Are SIEM platforms suitable for both large enterprises and SMEs? Yes, both large enterprises and small-to-medium businesses are increasingly adopting SIEM to strengthen their security posture and compliance readiness.​ 5. What trends are shaping SIEM adoption in Australia? AI-powered analytics, automation, and integration with SOAR are top trends, addressing complexity and improving response speeds in the face of rising threats.

Scroll to Top