cybersecurity

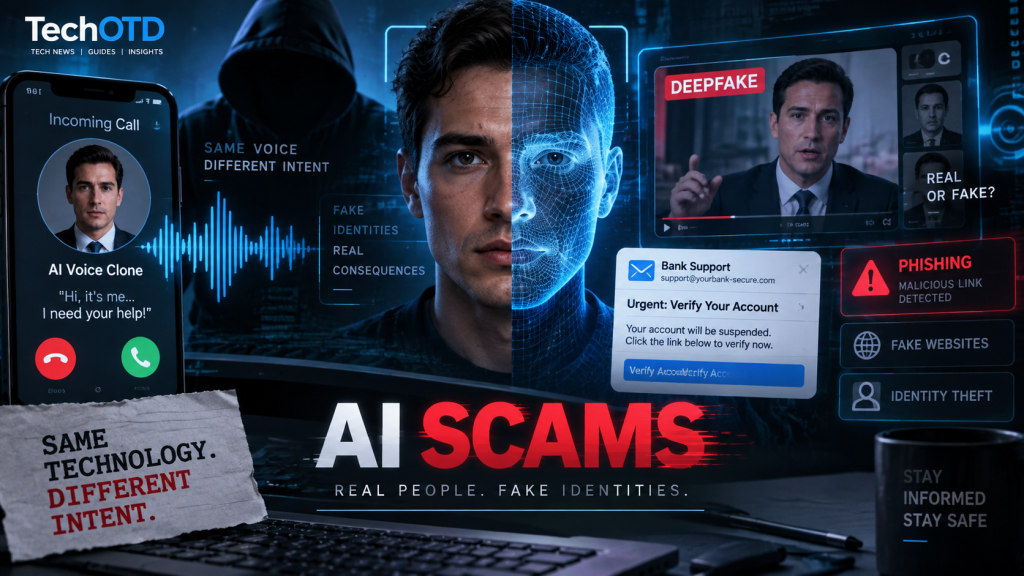
AI scams in 2026 using deepfakes, voice cloning, phishing, and fake identities
Artificial Intelligence

AI Scams in 2026: How Technology Is Making Scams Harder to Detect

Artificial intelligence is changing the way we work, communicate, and do business. But the same technology is also giving scammers powerful new ways to deceive people. From AI-generated phishing messages and cloned voices to deepfake videos and highly personalized fraud, scams are becoming harder to recognize than ever. In 2026, AI scams are no longer limited to obvious fake messages. Attackers can use AI to imitate trusted people, create convincing websites, generate realistic audio and video, and personalize scams at scale. This makes traditional warning signs less reliable and increases the need for smarter prevention. The good news is that AI can also be used to fight back. AI-powered fraud detection, behavioral analysis, deepfake detection, and real-time scam monitoring can help individuals and businesses identify suspicious activity before it causes serious damage. In this article, we’ll explore how AI-powered scams work, why they are becoming harder to detect, and how technology and practical security habits can help prevent them. What Are AI-Powered Scams? AI-powered scams are fraudulent activities that use artificial intelligence to make scams more convincing, personalized, or difficult to detect. Instead of relying only on traditional scripts and fake messages, scammers can now use AI to generate realistic text, images, audio, video, and even fake identities. For example, a scammer can use AI to create a convincing phishing email that looks like it came from a bank, generate a voice that sounds like a family member, or create a deepfake video of a trusted person. These technologies allow criminals to make their attacks appear much more legitimate. The biggest change is the scale and speed of these attacks. AI allows scammers to create personalized content for thousands of targets with far less effort than before. This makes AI-powered fraud a growing challenge for individuals, businesses, financial institutions, and online platforms. How Scammers Are Using AI 1. AI-Generated Phishing Messages AI can generate highly convincing phishing emails, text messages, and social media messages within seconds. Scammers can customize these messages using information about a person’s job, interests, recent activities, or relationships, making fraudulent communication appear more legitimate. 2. Voice Cloning and Impersonation Voice cloning technology can reproduce a person’s voice from a relatively short audio sample. Scammers can use cloned voices to impersonate family members, company executives, customer support agents, or other trusted individuals and create urgent requests for money or sensitive information. 3. Deepfake Videos and Images AI-generated images and deepfake videos can make it appear as though a real person said or did something they never actually did. Scammers may use this technology to impersonate public figures, business leaders, or people known to the victim. 4. Fake Websites and AI-Generated Content Generative AI can help scammers create professional-looking websites, advertisements, product descriptions, and fake customer support conversations. When combined with stolen logos and copied branding, these websites can be difficult to distinguish from legitimate services. 5. Personalized Scams at Scale One of AI’s biggest advantages for scammers is automation. Instead of sending the same message to everyone, criminals can generate different messages for different targets. This makes scams more personalized while allowing attackers to reach a much larger number of people. Most Common AI Scams in 2026 AI-powered scams can take many forms, depending on the technology being used and the information available to the attacker. Some scams target individuals directly, while others are designed to manipulate employees, customers, or entire organizations. AI Voice Scams Scammers can use AI voice cloning to imitate someone the victim knows or trusts. A fake emergency call from a family member or an urgent payment request from a senior executive can create pressure to act without verification. Deepfake Investment Scams Deepfake videos and AI-generated content can be used to make fake investment opportunities appear credible. Scammers may impersonate business leaders, financial experts, or public figures to encourage victims to send money or share financial information. AI-Powered Phishing Scams AI makes it easier for scammers to create phishing messages that look professional and contain fewer obvious spelling or grammar mistakes. These messages may imitate banks, delivery companies, employers, government services, or popular online platforms. Fake Customer Support Scams Scammers can use AI-generated websites, chatbots, and social media profiles to imitate legitimate customer support services. Victims may be tricked into revealing passwords, verification codes, payment details, or other sensitive information. Romance and Social Engineering Scams AI can help scammers maintain convincing conversations for longer periods and personalize their communication based on information gathered from social media. This can make fake relationships, investment requests, or emotional manipulation much more difficult to recognize. Why AI Scams Are Harder to Detect Traditional scams often contain obvious warning signs such as poor grammar, generic messages, suspicious links, or unrealistic offers. AI can remove many of these clues by generating polished, natural-sounding, and highly targeted content. AI also makes impersonation more convincing. A cloned voice can sound like someone the victim knows, while a deepfake video can create the appearance of a real person speaking or appearing on camera. When a scam uses familiar identities and realistic communication, people may be more likely to trust it. Another challenge is speed. Scammers can use AI to create and modify fraudulent content quickly, test different approaches, and target large numbers of people. As AI-generated content becomes more realistic, relying only on visual or grammatical clues is no longer enough to identify every scam. How AI Can Help Prevent Scams While criminals are using AI to make scams more convincing, the same technology can also help detect and prevent fraud. AI systems can analyze large amounts of data, identify unusual patterns, and detect suspicious behavior much faster than traditional rule-based systems. Real-Time Scam Detection AI-powered security systems can analyze messages, websites, emails, and online interactions in real time. By identifying suspicious patterns and known indicators of fraud, these systems can warn users before they click a malicious link or share sensitive information. Behavioral Fraud Detection AI can learn normal user behavior and identify unusual activity. For example, an unexpected login, unusual transaction,
Artificial Intelligence, cybersecurity, Technology & Innovation

The Double-Edged Sword: How Artificial Intelligence is Rewriting the Rules of Cybersecurity

The Double-Edged Sword: How Artificial Intelligence is Rewriting the Rules of Cybersecurity We live in a world where our lives are fundamentally digital. From the photos of our kids stored in the cloud to the banking apps that hold our hard-earned savings, our digital footprints are massive. But behind the convenience of this connected world lies a chaotic, hidden battleground. Every single day, millions of cyberattacks are launched across the globe. Sneaky phishing emails, devastating ransomware, and massive corporate data breaches have become a regular part of our daily news cycle. For years, human security analysts were the primary defense line against these threats. But the sheer scale of the digital universe has outgrown human capacity. It’s like trying to drink from a firehose while playing a high-stakes game of Whack-A-Mole. Enter Artificial Intelligence (AI). AI has burst onto the scene as the ultimate savior for digital defense. It promises to analyze billions of data points in milliseconds, predict attacks before they happen, and patch vulnerabilities instantly. But there is a dark side to this story. The very same technology that shields us is also being weaponized by cybercriminals. Let’s dive deep into the fascinating, slightly terrifying, and incredibly fast-moving world of Artificial Intelligence in cybersecurity. We will explore how it works, how the bad guys are abusing it, and what the future holds for human defense teams. Part 1: Why Traditional Cybersecurity is Failing To truly appreciate why AI is a game-changer, we first have to understand why our old ways of doing things are falling apart. Traditionally, cybersecurity relied on something called signature-based detection. Think of it like a digital “Most Wanted” poster. When a security company discovered a new virus, they isolated its unique digital signature (a specific piece of code) and added it to a database. Your antivirus software would scan your computer, look for that specific signature, and block it if found. For a long time, this worked decently well. But it has two massive, fatal flaws: The “Zero-Day” Problem: Signature-based systems can only catch threats that have been seen before. If a hacker writes a brand-new piece of malware that isn’t in the database yet—known as a “Zero-Day” attack—the traditional software is completely blind to it. Alert Fatigue: Modern companies generate millions of security logs every day. Traditional software flags anything even slightly unusual, drowning human IT managers in a sea of alerts. When everything is a warning, nothing is a warning. Exhausted analysts inevitably miss the real, dangerous threats buried in the noise. The reality is that hackers have evolved. They move at lightning speed, changing their code dynamically to bypass traditional filters. Human beings simply cannot type, think, or react fast enough to keep up. We needed a system that doesn’t just look backward at past threats, but one that can think, adapt, and predict in real-time. Part 2: How AI Transforms Cyber Defense AI doesn’t sleep, it doesn’t get tired, and it doesn’t suffer from alert fatigue. By leveraging machine learning models, modern cybersecurity systems have shifted from a reactive stance to a proactive one. Here is exactly how AI is changing the defensive landscape. 1. Behavioral Analysis (Anomalous Activity Detection) Instead of looking for specific bad code, AI looks at behavior. It starts by learning what “normal” looks like for a specific network or user. For instance, it learns that Sarah from Accounting typically logs in from Chicago at 9:00 AM, uses Microsoft Excel, and downloads about 50 megabytes of data a day. If Sarah suddenly logs in at 3:00 AM from an IP address in eastern Europe and attempts to download 40 gigabytes of sensitive source code, the AI immediately flags it. Even if the hacker has Sarah’s valid username and password, the AI recognizes the behavior as highly anomalous and locks down the account instantly. 2. Automated Incident Response When a cyberattack hits, seconds matter. If a ransomware strain begins encrypting files on a company server at 2:00 AM on a Sunday, waiting for a human technician to wake up, check their email, drive to the office, and pull the plug could mean total devastation. AI-driven security systems can execute SOAR (Security Orchestration, Automation, and Response) playbooks. The moment an attack is detected, the AI can automatically isolate the infected computer from the rest of the network, block the malicious IP address, and preserve the data logs for investigation. It mitigates the damage in milliseconds, long before a human can even open their eyes. 3. Predictive Threat Intelligence AI excels at finding patterns in chaos. By scraping data from global security feeds, forums, and even the dark web, AI can predict where hackers are likely to strike next. It scans an organization’s public-facing infrastructure, identifies weak spots (like unpatched software), and tells the IT team precisely what they need to fix before malicious actors find it. Part 3: The Dark Side — When Hackers Use AI Technology is inherently neutral; it is defined by the intent of the person using it. Unfortunately, the exact same AI capabilities that make defenses stronger are giving cybercriminals unprecedented superpowers. We have officially entered the era of AI vs. AI warfare. Here is how the bad guys are exploiting Artificial Intelligence. 1. Hyper-Realistic Phishing and Social Engineering We all know the classic phishing email: full of terrible grammar, weird fonts, and a glaringly obvious fake link from a “Nigerian Prince” or a “bank manager” asking you to update your details. They were relatively easy to spot. Not anymore. Generative AI tools like ChatGPT have made it incredibly easy for hackers—even those who don’t speak English well—to write flawless, highly persuasive, and professionally phrased emails. Worse yet, hackers can use AI to crawl an individual’s public social media profiles (LinkedIn, Twitter, Facebook) to gather personal details. The AI can then automatically generate a highly tailored, deeply convincing email customized just for them. This is called Spear Phishing, and when powered by AI, its success rate skyrockets. 2. Deepfakes: The Next Frontier of

Cybersecurity team analyzing AI-driven cyber attack patterns, phishing threats, deepfakes, and adaptive malware risks on a digital dashboard.
cybersecurity

How Cyber Attacks Are Changing in the Age of AI

Introduction Cyber attacks have always evolved alongside technology, but AI has changed the pace and scale of that evolution. What once required skilled attackers, long preparation, and manual effort can now be partially or fully automated, allowing criminals to launch more attacks in less time. This means organizations are no longer dealing with isolated threats; they are facing industrialized cybercrime that can adapt quickly and target more victims at once. One of the biggest shifts is in social engineering. AI makes phishing messages sound more natural, personalized, and believable, which increases the chances that people will click, reply, or share sensitive information. Attackers are also using deepfake audio and video to impersonate executives, coworkers, or trusted contacts, turning identity fraud into a much more serious threat. AI is also improving the speed and precision of technical attacks. Criminals can use it to scan for vulnerabilities, optimize exploit attempts, and adjust malware behavior in real time. This makes attacks harder to stop because they can change their method as defenders respond. Another major change is that cyberattacks are becoming multi-channel. Instead of relying only on email, attackers now combine messaging apps, phone calls, collaboration tools, social platforms, and even legitimate authentication flows to reach targets. This creates a more realistic and coordinated attack path that is harder for users and security teams to recognize quickly. AI is also affecting the defensive side of security, because the same technology used by attackers can help defenders detect unusual behavior, analyze threats, and respond faster. But the overall risk is rising because attackers often move faster than organizations can adapt. As a result, cybersecurity teams are being pushed to focus more on prevention, identity verification, and resilience than on detection alone. Key changes Phishing is becoming more personalized and convincing. Deepfakes are making impersonation attacks more dangerous. Malware is becoming more adaptive and difficult to detect. Attacks are happening across more channels than email alone. Attackers are using AI to move faster than traditional defense teams. Conclusion Cyber attacks in the age of AI are faster, smarter, and more scalable than before. That means companies and individuals must become more careful about identity verification, suspicious messages, and security habits. The future of cyber defense will depend on using AI wisely, improving awareness, and building systems that can stop attacks before they spread. In this new environment, speed matters on both sides, but defense must become more proactive and resilient.extension. FAQ How is AI changing cyber attacks? AI is making attacks more automated, personalized, and difficult to detect by helping attackers create better phishing, deepfakes, malware, and multi-channel campaigns. What is the most common AI-powered attack? Phishing is one of the most common because AI can make messages sound more believable and targeted. Are deepfakes really a cybersecurity threat? Yes, deepfakes can be used to impersonate leaders, employees, or trusted contacts and trick people into sharing money or information. Can AI help defenders too? Yes, AI can help security teams detect threats, analyze patterns, and respond faster, but attackers are also using it aggressively. Why are AI attacks harder to stop? They are harder to stop because they can adapt in real time, operate across many channels, and move at machine speed. What should businesses do now? Businesses should improve employee awareness, verify identities carefully, strengthen security controls, and prepare for more advanced AI-driven threats.

Business team reviewing cybersecurity strategies to protect company data, systems, and customer trust.
cybersecurity

Why Cybersecurity Should Be a Priority for Every Company

Introduction In today’s connected world, nearly every company relies on technology to store data, communicate with customers, process payments, manage employees, and run daily operations. That dependence makes cybersecurity essential, not optional, because every digital interaction creates some level of risk. Whether a business is a small startup or a large enterprise, it holds information that attackers may want, including financial records, customer details, login credentials, and internal documents. Cybersecurity should be a top priority for every company because modern businesses depend on digital systems, and even one weak point can lead to data loss, downtime, financial damage, and a broken reputation. As cyber threats become more frequent and sophisticated, companies that ignore security are putting both operations and customer trust at risk. One reason cybersecurity matters so much is that cyberattacks can cause immediate and lasting harm. A breach can shut down systems, interrupt business continuity, expose sensitive information, and lead to expensive recovery efforts. Beyond the technical damage, companies often face legal issues, customer frustration, and reputational loss that can take years to repair. Cybersecurity is also important because threats are no longer rare or simple. Attackers use phishing, ransomware, credential theft, and other methods that are designed to trick people and exploit weak systems. Many attacks succeed not because companies have no defenses at all, but because employees are not trained well enough or security practices are inconsistent across the organization. Another major reason to prioritize cybersecurity is trust. Customers, partners, and employees want to know that their data is being handled responsibly. When a company shows that it takes security seriously, it builds confidence and strengthens its brand, but when it suffers a breach, that trust can disappear very quickly. Cybersecurity also supports growth and innovation. Companies that feel protected are better able to adopt cloud tools, expand digital services, and automate more of their work without creating unnecessary exposure. In other words, strong security is not just about preventing problems; it is about creating a safer foundation for business growth. Why It Matters It protects sensitive data from theft or misuse. It reduces downtime and supports business continuity. It helps companies avoid financial and legal damage. It strengthens customer trust and brand reputation. It supports safe digital growth and innovation. Conclusion Cybersecurity should be a priority for every company because the cost of ignoring it is far higher than the cost of prevention. A strong security posture protects data, keeps operations running, and helps businesses maintain the trust they depend on. The companies that treat cybersecurity as part of their business strategy, not just an IT issue, are better prepared for the future. In a world where threats keep evolving, security is one of the smartest investments a business can make. FAQ Why is cybersecurity important for every company? Cybersecurity is important because every company stores data, uses digital tools, and faces cyber risks that can lead to loss, downtime, and reputational harm.online. What happens if a company ignores cybersecurity? A company may face data breaches, system outages, financial losses, legal problems, and a decline in customer trust. Is cybersecurity only important for large companies? No, small businesses are also targeted because attackers often look for weaker defenses. How does cybersecurity build customer trust? It shows customers that their data is protected and that the company is serious about responsibility and safety. What is one of the biggest cybersecurity risks? Phishing and ransomware are among the most common risks because they target both people and systems. How can companies improve cybersecurity? They can train employees, update systems, use strong access controls, and create a clear response plan for incidents.

Artificial Intelligence, Digital Transformation, Software development, Technology

Navigating the Next Tech Horizon: A Human Guide to the Innovations Reshaping Our Digital World

Introduction:- Remember when “the future” meant having a computer in your pocket? Today, we carry the processing power of a mid-90s supercomputer in our jeans, and yet we find ourselves standing on the precipice of an even more radical shift. The tech world isn’t just evolving; it’s rewriting its foundational code. As we navigate through 2026, the conversations around technology have shifted from basic automation to deep, systemic intelligence. We are no longer just building better tools; we are co-authoring a new reality with our machines. From the way developers write software to how global enterprises secure their data in the cloud, the digital landscape is undergoing a massive paradigm shift. Let’s pull back the curtain on the massive shifts defining the tech world today—broken down not just in code, but in human terms. 1. The Future of AI: Beyond the Chatbot Hype For a couple of years, the world was obsessed with generative AI that could write poems or generate quirky images. But the honeymoon phase is over. The future of AI isn’t about chatbots that mimic human speech; it’s about Agentic AI—autonomous systems capable of reasoning, planning, and executing complex workflows without constant human hand-holding. From Prompting to Partnering Early AI required meticulous prompting. If you didn’t phrase your question perfectly, the output was useless. Today, AI has developed contextual awareness. We are moving from a “command-and-control” dynamic to a truly collaborative partnership. Autonomous Agents: Imagine an AI assistant that doesn’t just book a flight when asked, but monitors your calendar, anticipates a business conflict, negotiates a rescheduled meeting with a client’s AI assistant, and books the optimal flight based on your historical preferences—all in the background. Multimodal Maturity: AI now naturally processes voice, video, text, and physical gestures simultaneously. This has broken down the barriers between digital intent and physical execution. The Human Element: Emotional Intelligence (EQ) Meets AI As AI handles the heavy analytical lifting, the premium on human emotional intelligence has skyrocketed. The most successful implementations of AI aren’t those that replace humans, but those that augment human empathy, creativity, and ethical judgment. We are the directors; AI is the ultimate crew. 2. Next-Gen Software Development: The Democratization of Code The software engineering landscape is experiencing its most significant disruption since the invention of high-level programming languages. Next-gen software development is defined by a symbiosis between human intuition and AI-driven development engines. The Rise of the “Architect” Mindset Writing syntax—the actual typing of loops, brackets, and boilerplate code—is increasingly being handled by AI co-pilots. Does this mean software engineers are obsolete? Absolutely not. Instead, their role has elevated. [Traditional Development] ──> Focus on Syntax, Debugging, & Boilerplate [Next-Gen Development] ──> Focus on Architecture, System Design, & Security Developers are transitioning from code writers to system architects. The value shifts from knowing how to write a function to understanding how systems interact, scale, and remain secure. Low-Code, No-Code, and the Citizen Developer We are seeing a massive democratization of technology. Business analysts, healthcare professionals, and educators are now building sophisticated enterprise applications using natural language interfaces. By bridging the gap between an idea and a working application, innovation is no longer bottlenecked by the availability of software engineering teams. 3. Cloud Computing Trends: The Distributed Cloud and Edge Renaissance The cloud is no longer a distant, centralized data center owned by a tech giant. Current cloud computing trends point toward a hyper-distributed model where data processing happens exactly where it makes the most sense. Edge Computing Comes of Age With the proliferation of IoT devices, smart cities, and autonomous vehicles, sending data back to a central cloud server introduces unacceptable latency. Example: An autonomous vehicle traveling at 60 mph cannot wait 200 milliseconds for a cloud server to process a “stop” command. The decision must happen at the “edge”—directly within the vehicle’s onboard processing unit. Sovereign Clouds and Data Privacy Geopolitics has firmly entered the cloud space. Nations and regions are demanding that their citizens’ data remain within geographical boundaries, governed by local laws. This has led to the rise of sovereign clouds, forcing global enterprises to rethink their infrastructure to ensure compliance without sacrificing performance. 4. Cyber Resilience: Shifting from Defense to Survival In the modern tech ecosystem, a data breach is no longer a matter of if, but when. Because of this harsh reality, the conversation has shifted from traditional cybersecurity (building taller walls) to cyber resilience (how well you can take a punch and keep standing). The Zero Trust Imperative The old security model assumed that everything inside a corporate network was safe. Today’s decentralized workforce has thoroughly shattered that perimeter. “Zero Trust” operates on a simple, human-like skepticism: Never trust, always verify. Every user, device, and connection must continuously prove its identity and authorization. Preparing for the Quantum Leap While practical quantum computers are still on the horizon, the cryptographic threat they pose is already reshaping current security strategies. Bad actors are actively harvesting encrypted data today, intending to decrypt it years later when quantum computing matures. Progressive organizations are already implementing Post-Quantum Cryptography (PQC) to ensure their data remains secure tomorrow. 5. Digital Transformation 2026: The Cultural Revolution True digital transformation 2026 isn’t about buying new software or migrating to the cloud just to tick a box. It is fundamentally a cultural shift that requires organizations to fundamentally reimagine how they deliver value to humans. Breaking Down Silos For decades, IT departments lived in isolation, speaking a language the rest of the business couldn’t comprehend. True digital transformation breaks these walls down. Technology is now deeply woven into every department—from HR using predictive analytics for talent retention, to marketing utilizing real-time AI generation for hyper-personalized campaigns. The Sustainability Metric Modern digital transformation is no longer just measured in ROI (Return on Investment), but also in its environmental impact. Data centers consume massive amounts of electricity and water. Forward-thinking companies are auditing their “digital carbon footprint,” optimizing their code for energy efficiency, and choosing cloud providers that run entirely on renewable

Artificial Intelligence, cybersecurity, Technology, Technology & Innovation

The New Cybersecurity Frontier: Defending Against AI-Driven Exploits and Autonomous Threats

The New Cybersecurity Frontier: Defending Against AI-Driven Exploits and Autonomous Threats The battleground of digital security has shifted from static defenses to dynamic, algorithmic warfare. For decades, the foundational rules of cybersecurity revolved around predictable patterns. A human attacker wrote malicious code, a security researcher analyzed its signature, and an enterprise deployed a patch or an antivirus definition to block it. This cat-and-mouse game was bounded by the limits of human speed, requiring human hours to discover vulnerabilities, write exploits, and configure defenses. That era has officially drawn to a close. The consumerization and rapid maturation of advanced artificial intelligence frameworks have handed both adversaries and defenders a radically new toolset. Today, security professionals are no longer just fighting human threat actors; they are confronting autonomous, self-learning software agents capable of executing multi-stage attacks at network speeds. When machine learning models can instantly scan millions of lines of code for zero-day vulnerabilities, dynamically mutate payload signatures to evade behavioral detection, and generate hyper-personalized social engineering campaigns at an industrial scale, traditional defensive measures collapse. The infrastructure of tomorrow cannot be protected by the manual workflows of yesterday. Understanding this new paradigm requires looking deep into how weaponized artificial intelligence operates, where it breaches existing defenses, and how enterprises must adapt to survive. The Anatomy of an AI-Driven Cyberattack To defend against an automated adversary, engineering teams must dissect how machine learning alters the traditional cyberkill chain. In a conventional attack blueprint, an offensive operation requires weeks of manual reconnaissance. Attackers trace network perimeters, map out employee organizational charts on professional networks, and carefully audit public-facing infrastructure for unpatched software versions. Artificial intelligence compresses this reconnaissance phase from weeks to seconds. Large language models and specialized code-analysis patterns can ingest massive swaths of public and private data, mapping out corporate attack surfaces with terrifying precision. An automated scanning agent can systematically probe an enterprise’s entire cloud footprint, identifying subtle logic flaws or forgotten API endpoints that a human analyst might overlook during a routine security audit. Once a vulnerability is identified, the weaponization phase begins. Historically, modifying an exploit to bypass a specific endpoint detection and response system required deep assembly-level knowledge and hours of trial and error. Weaponized AI models automate this entirely through a process known as polymorphic code mutation. The malicious agent evaluates the target environment’s defenses and dynamically alters its own structure—changing variable names, modifying execution flows, and encrypting payloads uniquely for that specific machine—ensuring that signature-based antivirus tools remain completely blind to the threat. The execution phase introduces the concept of autonomous decision-making in the wild. Traditional malware relies on a continuous back-and-forth connection with an external command-and-control server to receive instructions from a human operator. This network traffic is highly visible and often triggers behavioral alarms within modern network monitoring suites. An AI-driven malicious agent, however, carries its neural net logic directly within its payload. It can make independent, real-time decisions inside a compromised network—such as choosing when to lie dormant to avoid detection, which high-value databases to target for lateral movement, and how to quietly exfiltrate data without triggering data loss prevention systems. The Weaponization of Large Language Models and Deepfakes Beyond pure code execution, the intersection of generative artificial intelligence and social engineering represents one of the most immediate financial hazards to modern enterprises. Social engineering has always relied on human psychology, but it was historically limited by language barriers, stylistic inconsistencies, and the sheer time required to engage with targets. Generative text models have completely democratized the production of flawless phishing campaigns. Phishing emails used to be easy to spot, often plagued by broken grammar, generic greetings, and suspicious formatting. Today, specialized malicious LLMs can generate perfectly written, context-aware correspondence tailored to a specific target’s industry jargon, corporate hierarchy, and historical writing style. By scraping an executive’s public presentations, blog posts, and social media presence, an automated agent can construct emails that are virtually indistinguishable from legitimate corporate communications, drastically increasing the success rate of business email compromise attacks. Simultaneously, the maturation of synthetic audio and video generation—commonly referred to as deepfakes—has added an entirely new dimension to identity theft and corporate fraud. Threat actors no longer rely solely on written words to trick financial departments into executing fraudulent wire transfers. They deploy real-time voice cloning tools during active phone calls, mimicking the exact cadence, tone, and vocal characteristics of a company’s Chief Financial Officer or Chief Executive Officer. In advanced scenarios, attackers execute highly coordinated multi-media deceptions. They schedule video conference calls where an AI-generated avatar of a trusted corporate leader directs a mid-level manager to bypass standard verification protocols for an urgent, confidential corporate acquisition. The psychological impact of seeing a familiar face and hearing a familiar voice completely bypasses the traditional skepticism employees have been trained to maintain, revealing that the human element remains the most vulnerable interface in the corporate security stack. Vulnerabilities Inherent in the AI Lifecycle As companies rush to integrate artificial intelligence into their own products and internal workflows, they inadvertently introduce an entirely new category of software vulnerabilities. These are not standard software bugs like buffer overflows or SQL injections; they are flaws native to the data structures, training pipelines, and architectural design of machine learning systems. The first major vulnerability is data poisoning. Machine learning models are entirely products of the data they consume during training. If a threat actor managed to subtly corrupt the training dataset of an enterprise model—for instance, by injecting malicious code samples labeled as benign into an automated code-review model—the resulting neural network would inherently inherit that blind spot. The model would systematically approve malicious patterns in production, creating an architectural vulnerability that is incredibly difficult to detect through standard source-code analysis. The second critical risk vector is prompt injection, which specifically targets applications built on top of large language models. Because these systems process user inputs and system instructions within the same linguistic context window, an attacker can craft input strings that overwrite the model’s core

cybersecurity, Digital Transformation, Educational Technology, enterprise

Zero Trust Security: Why Organizations Are Adopting It Faster Than Ever

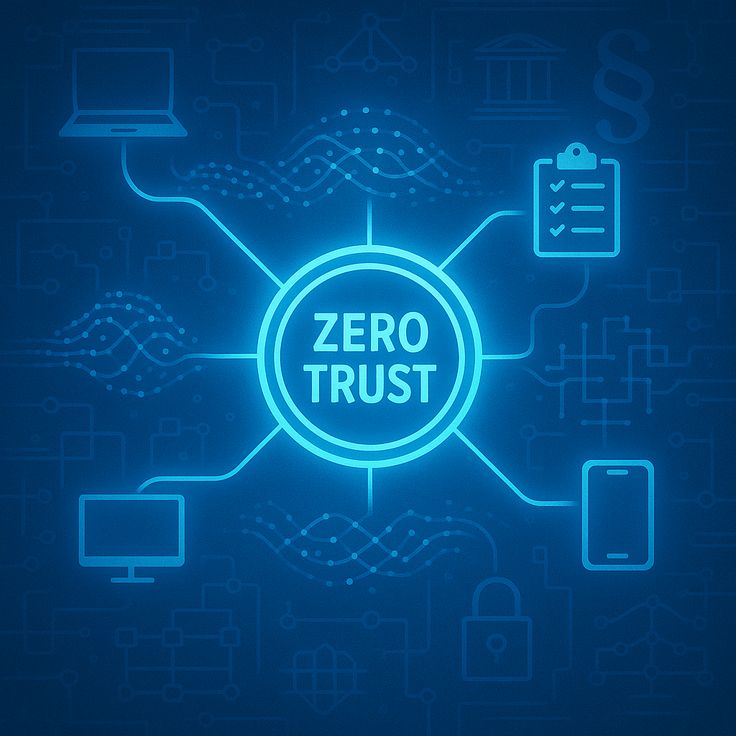
Zero Trust Security: Why Organizations Are Adopting It Faster Than Ever Cybersecurity has never been more important than it is today. Organizations across the globe are facing an unprecedented number of cyber threats, ranging from ransomware attacks and phishing campaigns to insider threats and sophisticated nation-state cyber operations. As businesses continue to embrace cloud computing, remote work, digital transformation, and interconnected technologies, traditional security models are proving increasingly inadequate. For decades, organizations relied on perimeter-based security strategies. The assumption was simple: anything inside the corporate network could be trusted, while anything outside should be treated as a potential threat. Firewalls, VPNs, and network segmentation formed the backbone of enterprise security. However, the modern digital environment has fundamentally changed this approach. Employees access company resources from multiple devices and locations. Applications reside in public and private clouds. Third-party vendors require network access. Sensitive data moves continuously between platforms and users. In this new reality, the concept of trust based solely on network location no longer works. This is where Zero Trust Security comes into the picture. Zero Trust has rapidly evolved from a cybersecurity concept into one of the most widely adopted security frameworks worldwide. Organizations of all sizes are investing heavily in Zero Trust architectures to protect their digital assets, strengthen compliance, and reduce cyber risks. But what exactly is Zero Trust Security, and why are organizations adopting it faster than ever before? Let’s explore. Understanding Zero Trust Security Zero Trust Security is a cybersecurity framework built on a simple but powerful principle: “Never Trust, Always Verify.” Unlike traditional security models that automatically trust users and devices inside a corporate network, Zero Trust assumes that every user, device, application, and connection could potentially be compromised. Under a Zero Trust model, no entity receives automatic trust, regardless of whether it is inside or outside the network perimeter. Every access request must be continuously verified before access is granted. This verification process typically includes: Identity verification Device authentication Access control policies User behavior analysis Multi-factor authentication Continuous monitoring The objective is to minimize risk by ensuring that only authorized users can access specific resources under predefined conditions. The Evolution of Cybersecurity Threats One of the biggest reasons organizations are embracing Zero Trust is the dramatic evolution of cyber threats. Modern cybercriminals have become more sophisticated than ever. Today’s attackers use advanced techniques such as: Ransomware-as-a-Service (RaaS) AI-powered phishing attacks Credential theft Supply chain attacks Insider threats Cloud account compromises Social engineering campaigns Many of these attacks bypass traditional security defenses because they exploit trusted accounts and legitimate access credentials. When attackers successfully steal login credentials, they can often move freely across traditional networks without triggering security alerts. Zero Trust eliminates this weakness by requiring verification at every stage of access. Even if an attacker compromises one account, they cannot automatically gain unrestricted access to sensitive systems. This significantly reduces the attack surface and limits potential damage. Why Traditional Security Models Are Failing The traditional “castle-and-moat” approach to cybersecurity was designed for a different era. In the past: Employees worked primarily from offices. Applications were hosted on-premises. Data remained within corporate networks. Devices were company-managed. Today, none of these assumptions consistently apply. Modern enterprises operate in highly distributed environments where: Employees work remotely. Applications run in multiple clouds. Data resides across various platforms. Contractors and vendors require access. Employees use personal devices. As a result, the network perimeter has effectively disappeared. Organizations can no longer rely solely on perimeter defenses because users and data exist far beyond traditional boundaries. Zero Trust addresses this challenge by focusing on identities, devices, and access rather than network location. The Core Principles of Zero Trust Security While Zero Trust implementations vary between organizations, most frameworks follow several key principles. Verify Every User Every user must authenticate before accessing resources. Authentication methods may include: Passwords Biometrics Security tokens Multi-factor authentication Identity verification is performed continuously rather than only during login. Least Privilege Access Users receive only the minimum access necessary to perform their tasks. This approach reduces risk because compromised accounts cannot access systems beyond their authorized permissions. Least privilege significantly limits lateral movement during cyberattacks. Continuous Monitoring Security teams continuously monitor user activities, devices, and network traffic. Behavior analytics help identify unusual patterns that may indicate malicious activity. Suspicious behavior triggers additional verification or access restrictions. Assume Breach Zero Trust operates under the assumption that breaches can occur at any time. Instead of focusing solely on prevention, organizations prioritize detection, containment, and response. This mindset improves resilience against sophisticated attacks. Device Security Verification Access decisions consider device health and security status. Devices may be evaluated based on: Operating system updates Antivirus status Encryption settings Security compliance Compromised or non-compliant devices may be denied access. The Remote Work Revolution Accelerated Adoption The global shift toward remote and hybrid work has dramatically accelerated Zero Trust adoption. Employees now access corporate resources from: Home offices Coffee shops Airports Co-working spaces Mobile devices Traditional VPN-based security approaches struggle to secure this distributed workforce effectively. Organizations need a security framework that protects users regardless of location. Zero Trust enables secure access by verifying users and devices rather than relying on network boundaries. As remote work becomes a permanent part of business operations, Zero Trust continues to gain momentum. Cloud Computing and Zero Trust Cloud adoption is another major driver behind the rise of Zero Trust Security. Modern organizations increasingly rely on: Software-as-a-Service (SaaS) Infrastructure-as-a-Service (IaaS) Platform-as-a-Service (PaaS) Cloud environments introduce new security challenges because resources are distributed across multiple providers and locations. Traditional security architectures often lack visibility and control in these environments. Zero Trust helps organizations secure cloud assets through: Strong identity management Granular access controls Continuous authentication Micro-segmentation Cloud workload protection This approach improves security without sacrificing flexibility. The Role of Multi-Factor Authentication Multi-factor authentication (MFA) has become a cornerstone of Zero Trust Security. Passwords alone are no longer sufficient. Attackers frequently obtain credentials through: Phishing attacks Data breaches Malware Credential stuffing MFA requires users to provide additional verification

Data Privacy & Security, Digital Transformation, Technology

Digital Sovereignty: Why Countries Want Greater Control Over Their Data

Digital Sovereignty: Why Countries Want Greater Control Over Their Data The digital economy has become one of the most valuable assets of the modern world. Every day, governments, businesses, and individuals generate enormous amounts of data through online transactions, cloud applications, social media platforms, connected devices, and artificial intelligence systems. Data now drives decision-making, economic growth, innovation, and national security. As technology becomes increasingly integrated into every aspect of society, many countries are asking a critical question: Who controls the data? This question has led to the rise of a concept known as digital sovereignty, a growing movement that seeks to give nations greater authority over their digital assets, infrastructure, and data. Governments worldwide are introducing policies and regulations designed to ensure that sensitive information remains protected and accessible according to national laws and interests. In 2026, digital sovereignty is no longer a niche policy discussion. It has become a central issue shaping technology strategies, international relations, cloud computing investments, and cybersecurity initiatives around the globe. What Is Digital Sovereignty? Digital sovereignty refers to a country’s ability to control its digital infrastructure, data, technologies, and online activities according to its own laws and regulations. The concept extends beyond simple data storage. It encompasses: Data ownership and governance Cloud infrastructure control Cybersecurity management Artificial intelligence regulation Digital identity systems Critical technology supply chains National internet policies In practical terms, digital sovereignty means ensuring that a country’s most important digital resources are not entirely dependent on foreign companies or governments. As digital technologies become essential to national economies, countries increasingly view data as a strategic resource similar to energy, natural resources, or critical infrastructure. Why Data Has Become a Strategic National Asset For decades, oil was often described as the world’s most valuable resource. Today, many experts argue that data has taken its place. Data powers: Artificial intelligence models Financial systems Healthcare innovation Smart city initiatives National defense systems E-commerce platforms Public services The more data organizations collect, the more effectively they can optimize operations, understand customer behavior, and develop new technologies. Because of its value, governments are becoming increasingly concerned about where data is stored, who has access to it, and how it is used. Countries recognize that losing control over critical data could create economic, political, and security vulnerabilities. The Growing Importance of Data Localization One of the most visible aspects of digital sovereignty is data localization. Data localization policies require certain types of information to be stored and processed within national borders. Governments implement these policies for several reasons: National Security Protection Sensitive government information, military data, and critical infrastructure records must remain protected from external threats. Storing such information domestically allows governments to apply local security standards and oversight. Regulatory Compliance Countries often require businesses to comply with local privacy laws and regulations. Domestic data storage simplifies enforcement and legal accountability. Economic Development Local data centers create jobs, attract technology investments, and strengthen national digital ecosystems. As a result, many nations are investing heavily in domestic cloud infrastructure. Cybersecurity Concerns Are Driving Sovereignty Efforts Cyberattacks continue to grow in both frequency and sophistication. Governments face threats from: State-sponsored hackers Cybercriminal organizations Ransomware groups Espionage operations Supply chain attacks When critical systems rely heavily on foreign technology providers, governments may have limited visibility into potential risks. Digital sovereignty initiatives help countries strengthen cybersecurity by: Building secure national infrastructure Developing local cybersecurity expertise Establishing stronger data protection controls Reducing dependency on external providers As cyber warfare becomes an increasingly important national security issue, governments view digital control as a strategic necessity. The Role of Cloud Computing in Digital Sovereignty Cloud computing has transformed the way organizations store and process data. Major cloud providers offer scalability, reliability, and cost efficiency that many organizations cannot achieve independently. However, cloud adoption has also raised concerns about sovereignty. Many governments worry about: Foreign jurisdiction over stored data Cross-border data transfers Access requests from foreign authorities Dependence on a small number of global providers To address these concerns, cloud vendors are introducing sovereign cloud solutions that provide greater transparency, local control, and compliance capabilities. These offerings are becoming increasingly attractive to governments, healthcare organizations, financial institutions, and regulated industries. Artificial Intelligence and Sovereign Data Artificial intelligence has added a new dimension to digital sovereignty discussions. AI systems rely heavily on data for training and operation. Governments are concerned about several issues: Control of Training Data Countries want assurance that sensitive national data is not being used without permission to train foreign AI models. AI Governance Governments seek to establish rules regarding how AI systems are developed, deployed, and monitored. National Competitiveness Access to high-quality data can influence a country’s ability to compete in AI innovation. As AI becomes a key driver of economic growth, digital sovereignty strategies increasingly include AI infrastructure and data governance frameworks. How Different Regions Are Approaching Digital Sovereignty Countries are pursuing digital sovereignty in different ways based on their priorities and regulatory environments. Europe European nations have emphasized privacy protection, data governance, and regulatory compliance. The region has introduced comprehensive regulations designed to strengthen control over personal data while promoting transparency and accountability. European policymakers often focus on reducing strategic dependence on non-European technology providers. Asia-Pacific Many countries in the Asia-Pacific region are investing heavily in domestic cloud infrastructure, cybersecurity programs, and AI development. Several governments have introduced data localization requirements to enhance national security and economic resilience. North America While cloud adoption remains widespread, discussions around critical infrastructure protection, cybersecurity, and AI governance continue to influence digital sovereignty initiatives. Governments increasingly recognize the importance of maintaining control over strategic digital assets. Middle East The Middle East has become a major hub for digital transformation projects. Many countries are building advanced data centers and cloud ecosystems to support economic diversification and strengthen national digital capabilities. The Economic Impact of Digital Sovereignty Digital sovereignty is creating significant economic opportunities. Growth of Local Data Centers Demand for domestic data storage is driving investments in: Data center construction Renewable energy integration Cloud infrastructure

Artificial Intelligence, cybersecurity, Technology

The Future of Cybersecurity in the Age of Generative AI

The Future of Cybersecurity in the Age of Generative AI The cybersecurity landscape is undergoing a dramatic transformation. As organizations continue to embrace digital technologies, cloud computing, remote work, and interconnected systems, cyber threats are becoming increasingly sophisticated. At the same time, a new technological revolution is reshaping how businesses defend themselves against these threats: Generative Artificial Intelligence (Generative AI). Generative AI has rapidly evolved from a fascinating innovation into a powerful business tool capable of creating content, analyzing data, automating processes, and assisting with complex decision-making. While much of the public attention has focused on AI-generated text, images, and videos, one of its most significant impacts is emerging in the field of cybersecurity. Generative AI is creating both opportunities and challenges. On one hand, it enables organizations to detect threats faster, automate security operations, and strengthen defenses against cybercriminals. On the other hand, malicious actors are leveraging the same technology to launch more convincing phishing attacks, develop advanced malware, and exploit vulnerabilities at unprecedented speeds. As businesses prepare for the future, understanding the relationship between generative AI and cybersecurity has become essential. The future of digital security will be defined by how effectively organizations can harness AI while managing the risks it introduces. Understanding Generative AI in Cybersecurity Generative AI refers to artificial intelligence systems capable of creating new content, generating responses, producing code, and learning patterns from massive datasets. Unlike traditional AI systems that primarily analyze information, generative AI can actively create solutions, recommendations, and predictions based on its training. In cybersecurity, this capability opens new possibilities for threat detection, incident response, vulnerability management, and security automation. AI systems can analyze vast amounts of security data, identify suspicious activities, and provide actionable insights in real time. Security teams are increasingly overwhelmed by the volume of alerts generated by modern networks. Generative AI helps reduce this burden by filtering irrelevant alerts, prioritizing threats, and assisting analysts in understanding complex attack patterns. This shift allows security professionals to focus on strategic decision-making rather than spending valuable time on repetitive tasks. The Growing Complexity of Cyber Threats Cybercriminals continue to evolve their methods as organizations strengthen their defenses. Traditional cybersecurity approaches often struggle to keep pace with the scale and speed of modern attacks. Attack surfaces have expanded significantly due to cloud adoption, Internet of Things (IoT) devices, remote work environments, and digital transformation initiatives. Every connected device and application introduces potential vulnerabilities that attackers can exploit. Modern threats include: Advanced phishing campaigns Ransomware attacks Supply chain compromises Zero-day vulnerabilities Insider threats Credential theft Social engineering attacks The increasing sophistication of these threats requires equally advanced defense mechanisms. Generative AI provides organizations with the ability to analyze complex environments continuously and identify emerging risks before they become major incidents. AI-Powered Threat Detection and Prevention One of the most promising applications of generative AI in cybersecurity is threat detection. Traditional security systems often rely on predefined rules and known attack signatures. While effective against familiar threats, these systems may struggle to identify new or evolving attack techniques. Generative AI can analyze patterns across networks, endpoints, user behavior, and application activity to detect anomalies that may indicate malicious activity. For example, if an employee suddenly accesses sensitive data from an unusual location or begins transferring large volumes of information, AI systems can recognize the abnormal behavior and trigger alerts. The benefits include: Faster threat identification Reduced false positives Improved accuracy Real-time monitoring Continuous learning capabilities By identifying threats earlier in the attack lifecycle, organizations can minimize damage and reduce recovery costs. Automating Security Operations Security operations centers (SOCs) face significant challenges due to staffing shortages and increasing workloads. Many organizations struggle to hire enough cybersecurity professionals to manage growing security demands. Generative AI can help bridge this gap by automating routine tasks and supporting security teams. AI-driven automation can assist with: Log analysis Incident classification Threat intelligence gathering Vulnerability assessment Security reporting Compliance monitoring Instead of manually reviewing thousands of alerts each day, analysts can rely on AI-powered systems to summarize incidents, recommend actions, and prioritize critical threats. This automation improves efficiency while enabling security teams to respond more quickly to potential attacks. The Role of Generative AI in Incident Response When a cyberattack occurs, rapid response is critical. Every minute of delay can increase financial losses, operational disruptions, and reputational damage. Generative AI can significantly accelerate incident response processes. AI systems can analyze attack data, identify affected systems, determine the likely attack path, and generate recommended remediation steps. Security teams can use AI-generated insights to: Investigate incidents faster Contain threats more effectively Reduce downtime Improve recovery processes Document incidents automatically As AI technologies continue to mature, organizations may increasingly rely on autonomous response systems capable of taking immediate defensive actions without human intervention. Predictive Cybersecurity and Risk Assessment One of the most exciting developments in AI-driven security is predictive threat analysis. Rather than simply reacting to attacks after they occur, organizations can use generative AI to anticipate future threats. By analyzing historical attack data, vulnerability trends, industry intelligence, and global threat activity, AI systems can identify potential risks before they are exploited. Predictive cybersecurity enables businesses to: Prioritize security investments Patch vulnerabilities proactively Strengthen high-risk systems Improve risk management strategies Reduce attack exposure This proactive approach represents a significant shift from traditional reactive security models. How Cybercriminals Are Using Generative AI While generative AI offers powerful defensive capabilities, it also provides new tools for cybercriminals. Attackers are increasingly using AI technologies to enhance their operations and improve attack success rates. Some malicious applications include: AI-Generated Phishing Attacks Traditional phishing emails often contain grammatical errors and suspicious language. Generative AI can produce highly convincing messages that closely resemble legitimate communications. These personalized attacks can be tailored to specific individuals, making them significantly harder to detect. Advanced Social Engineering AI can generate realistic conversations, fake identities, and persuasive messages designed to manipulate victims into revealing sensitive information. Automated Malware Development Cybercriminals may use AI-assisted coding tools to create malware variants more quickly and

Digital Transformation, enterprise, Technology

The Role of Digital Trust in Modern Enterprise Technology

Introduction In today’s hyperconnected digital world, technology has become the foundation of almost every business operation. Organizations rely on cloud platforms, artificial intelligence, automation, data analytics, and digital communication tools to improve efficiency and deliver better customer experiences. While these technologies offer tremendous opportunities, they also introduce new challenges related to security, privacy, transparency, and accountability. As a result, digital trust has emerged as one of the most important assets for modern enterprises. Digital trust refers to the confidence that customers, employees, partners, and stakeholders place in an organization’s ability to protect data, secure systems, and use technology responsibly. It goes beyond traditional cybersecurity and encompasses ethical technology practices, transparent data management, regulatory compliance, and reliable digital experiences. In an era where data breaches, cyberattacks, and privacy concerns regularly make headlines, organizations that establish strong digital trust gain a significant competitive advantage. Modern consumers are more informed than ever before. They expect businesses to handle their personal information responsibly and provide secure digital interactions. A single security incident can damage a company’s reputation, reduce customer loyalty, and lead to substantial financial losses. On the other hand, organizations that prioritize trust can strengthen relationships, improve customer retention, and accelerate digital transformation initiatives. Understanding Digital Trust Digital trust is the assurance that technology systems, processes, and organizations operate securely, reliably, and ethically. It is built through a combination of technological safeguards, transparent business practices, and consistent user experiences. When customers interact with a company’s website, mobile application, or digital service, they expect their data to remain protected. They want to know how their information is collected, stored, and used. Similarly, employees rely on secure digital environments to perform their work effectively, while business partners need confidence that shared information will remain protected. Digital trust is not created overnight. It requires continuous investment in cybersecurity, data governance, compliance programs, and ethical technology practices. Organizations must demonstrate that they are committed to safeguarding stakeholder interests while leveraging technology for innovation and growth. Why Digital Trust Matters More Than Ever The rapid expansion of digital technologies has significantly increased the volume of sensitive information being generated and processed. Businesses collect customer data, financial records, operational metrics, and proprietary intellectual property on a massive scale. As digital ecosystems become more interconnected, the risks associated with data misuse and cyber threats continue to grow. Several factors have contributed to the growing importance of digital trust: Rising Cybersecurity Threats Cybercriminals are constantly developing sophisticated attack methods targeting businesses of all sizes. Ransomware attacks, phishing campaigns, identity theft, and data breaches have become common challenges across industries. Organizations that fail to implement adequate security measures risk losing customer confidence and facing severe financial consequences. Increasing Privacy Expectations Consumers are becoming more aware of how companies collect and use their personal information. They expect transparency and control over their data. Businesses that respect privacy preferences and communicate their practices clearly are more likely to earn customer trust. Expansion of Artificial Intelligence Artificial intelligence is transforming decision-making processes across industries. However, concerns about algorithmic bias, transparency, and accountability have raised questions about how AI systems should be deployed responsibly. Trustworthy AI practices are becoming essential for maintaining stakeholder confidence. Regulatory Compliance Requirements Governments and regulatory bodies worldwide have introduced stricter regulations related to data protection and cybersecurity. Compliance is no longer optional. Organizations must demonstrate responsible data management practices to avoid legal penalties and reputational damage. Remote and Hybrid Work Models The rise of remote work has expanded digital attack surfaces. Employees access corporate systems from multiple locations and devices, increasing security risks. Building digital trust requires ensuring secure access and protecting sensitive information regardless of where work takes place. Key Pillars of Digital Trust Building digital trust requires a comprehensive approach that addresses multiple aspects of enterprise technology. Cybersecurity Cybersecurity forms the foundation of digital trust. Organizations must protect their systems, networks, and data from unauthorized access and malicious attacks. This includes implementing advanced security technologies such as multi-factor authentication, endpoint protection, encryption, and continuous monitoring. A strong cybersecurity strategy not only reduces risk but also demonstrates a company’s commitment to protecting stakeholder information. Data Privacy Privacy has become a major concern for consumers and regulators alike. Businesses must clearly explain how data is collected, stored, shared, and processed. Transparent privacy policies and user consent mechanisms help establish confidence and foster trust. Organizations should adopt privacy-by-design principles, ensuring that privacy considerations are integrated into technology development from the beginning. Transparency Trust grows when organizations are open about their practices and decision-making processes. Transparency involves communicating clearly about data usage, security measures, AI-driven decisions, and incident response procedures. When issues occur, transparent communication helps maintain credibility and demonstrates accountability. Reliability and Performance Customers expect digital services to be available, responsive, and dependable. Frequent system outages, technical failures, or poor user experiences can quickly erode trust. Modern enterprises must invest in infrastructure resilience, disaster recovery planning, and performance optimization to ensure consistent service delivery. Ethical Technology Use The ethical use of technology is becoming increasingly important. Organizations must ensure that AI systems, automation tools, and analytics platforms operate fairly and responsibly. Ethical technology practices include addressing algorithmic bias, ensuring explainability, and preventing misuse of customer data. Businesses that prioritize ethics strengthen their reputation and foster long-term trust. The Relationship Between Digital Trust and Business Success Digital trust is no longer just a technology concern; it is a business strategy. Organizations that successfully build trust often experience measurable benefits across multiple areas. Enhanced Customer Loyalty Customers are more likely to engage with brands they trust. When users feel confident that their information is secure and handled responsibly, they are more willing to share data and use digital services. Trust creates stronger customer relationships, leading to increased retention and higher lifetime value. Competitive Differentiation In crowded markets, trust can become a powerful differentiator. Organizations that demonstrate superior security, transparency, and ethical practices stand out from competitors. Customers increasingly consider trustworthiness when choosing products, services, and business partners. Accelerated Digital Transformation Digital transformation initiatives

Scroll to Top