
Phishing

Cybersecurity team analyzing AI-driven cyber attack patterns, phishing threats, deepfakes, and adaptive malware risks on a digital dashboard.
cybersecurity

How Cyber Attacks Are Changing in the Age of AI

Introduction Cyber attacks have always evolved alongside technology, but AI has changed the pace and scale of that evolution. What once required skilled attackers, long preparation, and manual effort can now be partially or fully automated, allowing criminals to launch more attacks in less time. This means organizations are no longer dealing with isolated threats; they are facing industrialized cybercrime that can adapt quickly and target more victims at once. One of the biggest shifts is in social engineering. AI makes phishing messages sound more natural, personalized, and believable, which increases the chances that people will click, reply, or share sensitive information. Attackers are also using deepfake audio and video to impersonate executives, coworkers, or trusted contacts, turning identity fraud into a much more serious threat. AI is also improving the speed and precision of technical attacks. Criminals can use it to scan for vulnerabilities, optimize exploit attempts, and adjust malware behavior in real time. This makes attacks harder to stop because they can change their method as defenders respond. Another major change is that cyberattacks are becoming multi-channel. Instead of relying only on email, attackers now combine messaging apps, phone calls, collaboration tools, social platforms, and even legitimate authentication flows to reach targets. This creates a more realistic and coordinated attack path that is harder for users and security teams to recognize quickly. AI is also affecting the defensive side of security, because the same technology used by attackers can help defenders detect unusual behavior, analyze threats, and respond faster. But the overall risk is rising because attackers often move faster than organizations can adapt. As a result, cybersecurity teams are being pushed to focus more on prevention, identity verification, and resilience than on detection alone. Key changes Phishing is becoming more personalized and convincing. Deepfakes are making impersonation attacks more dangerous. Malware is becoming more adaptive and difficult to detect. Attacks are happening across more channels than email alone. Attackers are using AI to move faster than traditional defense teams. Conclusion Cyber attacks in the age of AI are faster, smarter, and more scalable than before. That means companies and individuals must become more careful about identity verification, suspicious messages, and security habits. The future of cyber defense will depend on using AI wisely, improving awareness, and building systems that can stop attacks before they spread. In this new environment, speed matters on both sides, but defense must become more proactive and resilient.extension. FAQ How is AI changing cyber attacks? AI is making attacks more automated, personalized, and difficult to detect by helping attackers create better phishing, deepfakes, malware, and multi-channel campaigns. What is the most common AI-powered attack? Phishing is one of the most common because AI can make messages sound more believable and targeted. Are deepfakes really a cybersecurity threat? Yes, deepfakes can be used to impersonate leaders, employees, or trusted contacts and trick people into sharing money or information. Can AI help defenders too? Yes, AI can help security teams detect threats, analyze patterns, and respond faster, but attackers are also using it aggressively. Why are AI attacks harder to stop? They are harder to stop because they can adapt in real time, operate across many channels, and move at machine speed. What should businesses do now? Businesses should improve employee awareness, verify identities carefully, strengthen security controls, and prepare for more advanced AI-driven threats.
Digital padlock representing cybersecurity and data protection.
cybersecurity, Data Privacy & Security

Cybersecurity in the Digital Age: Protecting Data in a Connected World

Introduction We live in an age where data travels faster than thought — from cloud storage to smartphones, from online banking to social media. But as our digital world expands, so do the cyber threats lurking behind every connection. From global ransomware attacks to phishing scams and data breaches, cybercrime has evolved into one of the biggest challenges of the 21st century. In 2024 alone, the global cost of cybercrime was estimated to surpass $10 trillion, making it more profitable than the illegal drug trade. In this digital age, cybersecurity isn’t optional — it’s essential for individuals, businesses, and governments alike. What Is Cybersecurity? Cybersecurity refers to the practice of protecting systems, networks, and data from unauthorized access, attacks, and damage. It involves technologies, processes, and best practices designed to secure: Computers and servers Mobile devices Networks Cloud environments User data Core Objectives of Cybersecurity — The CIA Triad: Element Meaning Purpose Confidentiality Keeping data private Prevent unauthorized access Integrity Maintaining data accuracy Ensure data isn’t altered maliciously Availability Ensuring accessibility Keep systems online and functional Together, these principles form the foundation of all cybersecurity systems. ⚙️ Types of Cybersecurity Cybersecurity covers a wide range of protection layers designed to defend different parts of the digital ecosystem. 1. Network Security Protects internal networks from intruders using firewalls, intrusion detection systems, and VPNs. 2. Information Security (InfoSec) Ensures data privacy and protects sensitive information from leaks or misuse. 3. Cloud Security Secures cloud-based infrastructure, applications, and data stored in remote servers. 4. Endpoint Security Defends devices such as laptops, phones, and IoT gadgets that connect to a network. 5. Application Security Prevents vulnerabilities during software development through encryption, code testing, and patch management. 6. Operational Security (OpSec) Focuses on the policies and procedures to handle data and protect assets. 7. Disaster Recovery and Business Continuity Ensures systems can recover quickly from attacks or data loss events. Common Cyber Threats Cyberattacks come in many forms — some target individuals, others target global corporations. Here are the most common types of cyber threats: Type Description Example Phishing Fraudulent emails trick users into revealing credentials Fake bank alerts Ransomware Encrypts data and demands payment WannaCry, LockBit Malware Software designed to damage or steal information Viruses, Trojans Denial of Service (DoS/DDoS) Overloads servers to make them crash Attacks on websites or networks Man-in-the-Middle (MitM) Intercepts data during transmission Wi-Fi eavesdropping SQL Injection Inserts malicious code into databases Web form exploits Zero-Day Exploit Targets unpatched vulnerabilities Newly discovered software flaws Insider Threats Employees misuse access privileges Data theft by insiders The increasing sophistication of cyberattacks means no organization is immune — prevention and vigilance are key. Essential Cybersecurity Tools Modern cybersecurity strategies rely on a mix of software, AI, and human expertise. Commonly Used Tools: Antivirus Software: Protects against malware and viruses (e.g., Bitdefender, Norton) Firewalls: Blocks unauthorized access to networks Encryption Tools: Secures data in transit and at rest Password Managers: Protects user credentials VPNs: Masks IP addresses for secure browsing Intrusion Detection Systems (IDS): Monitors networks for suspicious activity Multi-Factor Authentication (MFA): Adds an extra security layer beyond passwords The Role of Artificial Intelligence in Cybersecurity AI is becoming a game-changer in the fight against cyber threats. How AI Helps: Detects anomalies in real-time Predicts potential attacks before they occur Automates incident response Reduces false alerts and improves accuracy Example: AI-driven tools like Darktrace and CrowdStrike use machine learning to identify unusual network behavior and block cyberattacks instantly. Cybersecurity in Business Organizations of all sizes — from startups to multinationals — are prime targets for hackers. Key Areas of Focus for Businesses: Employee Awareness Training: Human error is the top cause of breaches. Data Encryption: Sensitive data must be encrypted at all stages. Regular Security Audits: Identify vulnerabilities before hackers do. Zero-Trust Architecture: Verify every access attempt, even inside the network. Incident Response Plans: Prepare for attacks with structured recovery strategies. Example:In 2023, several global firms adopted Zero Trust Security Models, ensuring users and devices are verified every time they access company data — drastically reducing internal breaches. Cybersecurity in the Cloud With more organizations migrating to cloud services like AWS, Azure, and Google Cloud, securing cloud infrastructure is vital. Cloud security ensures: Data encryption Identity and access management (IAM) Secure APIs and regular patching Providers also follow shared responsibility models, meaning both the provider and the client share the duty of maintaining security. Cybersecurity for Individuals Cybersecurity isn’t just for corporations — individuals must also stay alert. Personal Cyber Hygiene Tips: Use strong and unique passwords for every account. Enable two-factor authentication (2FA). Avoid clicking on suspicious links or attachments. Update software and systems regularly. Use secured Wi-Fi networks. Regularly back up important data. The Future of Cybersecurity The coming years will see cybersecurity evolve alongside AI, quantum computing, and the Internet of Things (IoT). 🔮 Key Future Trends: AI-powered threat detection Quantum encryption for unbreakable security Zero Trust Architecture becoming the global standard Biometric authentication (face, fingerprint, voice) Cyber resilience — not just prevention but rapid recovery Cybersecurity is no longer about building walls — it’s about creating adaptive, intelligent systems that learn and evolve faster than attackers. Conclusion In the digital era, data is power, and protecting it is non-negotiable. Cybersecurity is the first line of defense against a world of invisible threats. Whether it’s an individual securing personal data or a multinational corporation safeguarding billions of records, awareness and preparation are the strongest shields. As technology advances, so must our commitment to cybersecurity — ensuring a safer, more resilient digital future for everyone. FAQs 1. What is cybersecurity in simple terms?Cybersecurity is the protection of computers, networks, and data from digital attacks or unauthorized access. 2. Why is cybersecurity important?It prevents data theft, financial loss, and system damage caused by hackers or malware. 3. What are common cyber threats?Phishing, ransomware, malware, DDoS attacks, and insider threats are among the most common. 4. How can individuals improve cybersecurity?Use strong passwords, enable two-factor authentication, and avoid suspicious emails or downloads. 5.

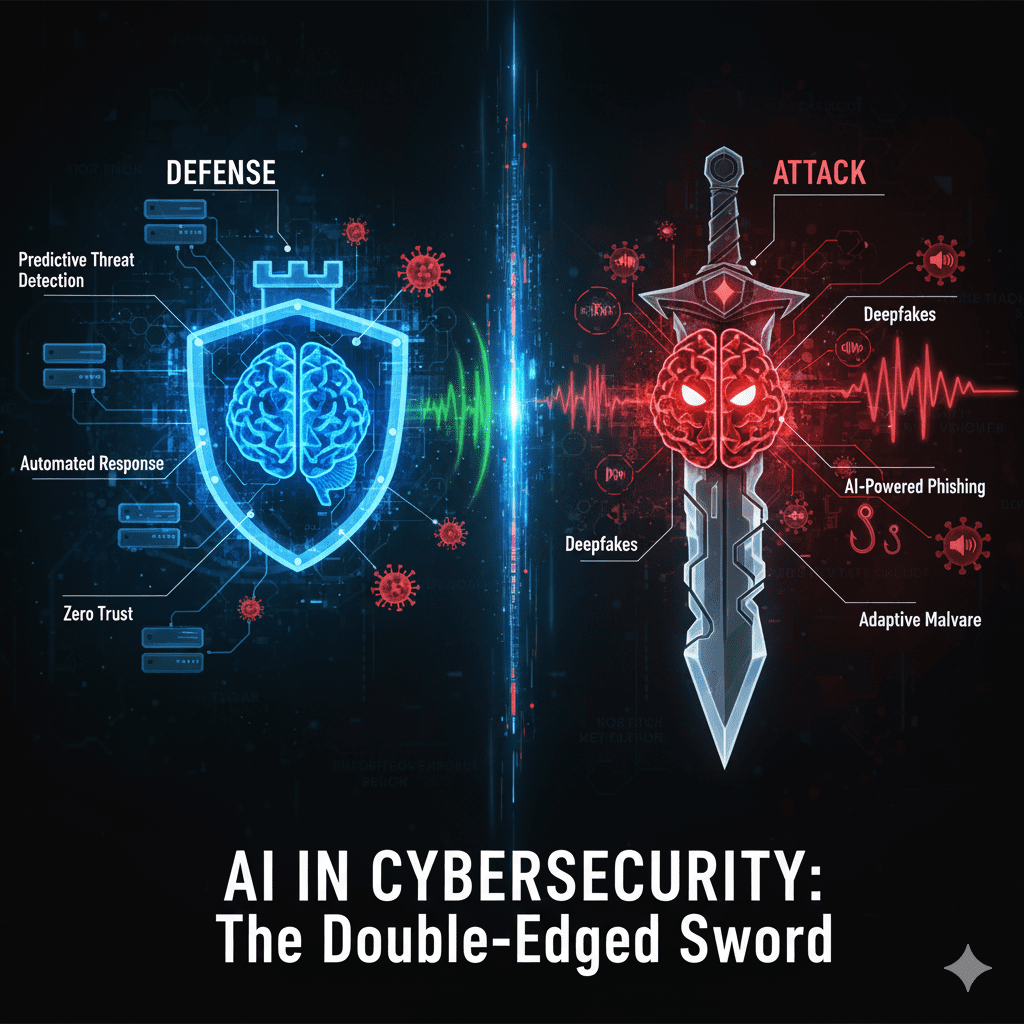
PREDICTIVE THREAT DETECTION and AUTOMATED RESPONSE
cybersecurity

Digital Armor: Defending Against Cyber Threats

Introduction For decades, the world of cybersecurity has been a high-stakes cat-and-mouse game. Security professionals build a wall, and hackers find a way over it. But today, this game is being fundamentally transformed by a powerful new player: Artificial Intelligence. AI is not just another tool; it’s a revolutionary force acting as both the strongest shield and the most dangerous new weapon. This article explores the dual role of AI in Cybersecurity, breaking down how it’s creating unprecedented defenses while simultaneously arming attackers with terrifying new capabilities The New Shield: AI as a Defensive Powerhouse The primary advantage of AI in a defensive role is its ability to process and analyze data at a scale and speed no human team could ever hope to match. While a human analyst sleeps, an AI security model is monitoring billions of events, looking for the one tiny anomaly that signals an attack. 1. Predictive Threat Detection Before AI, most security systems were reactive. They relied on “signatures”—the digital fingerprints of known malware. This meant a virus had to successfully attack someone first before it could be identified and blocked. AI, specifically machine learning, is predictive. It learns the normal, baseline behavior of your network, your users, and your devices. It can then spot suspicious deviations before a full-blown breach occurs. This includes: Behavioral Analysis: Is a user account that normally works from 9-to-5 suddenly trying to access sensitive files at 3:00 AM from a different country? AI flags this instantly. Anomaly Detection: Does a “smart” device like a thermostat suddenly start trying to communicate with an unknown server? AI can see this as a potential IoT (Internet of Things) attack. Pattern Recognition: AI can analyze global threat feeds and identify new attack patterns as they emerge, proactively blocking them before they even reach your network. 2. Automated Incident Response In a cyberattack, every second counts. A ransomware attack can encrypt an entire company’s files in minutes. AI doesn’t need to wait for approval; it can act in milliseconds. This is known as SOAR (Security Orchestration, Automation, and Response). Here’s a typical automated response scenario: Detect: An AI-powered sensor identifies a new, unknown program exhibiting ransomware-like behavior (e.g., rapidly encrypting files) on an employee’s laptop. Isolate: The AI immediately executes a predefined rule: it automatically disconnects that specific laptop from the company network, containing the threat. Investigate: The AI gathers all relevant data—what the program was, where it came from, what files it touched—and creates a report. Alert: It then sends an alert to a human security analyst, presenting the report and the action it took. The threat is neutralized before it could spread. The Future: An AI vs. AI Battleground This leads to an inevitable future: the front line of AI in Cybersecurity will be an AI-versus-AI battle. It will be a silent, high-speed war fought in milliseconds, with defensive AI models trying to detect and stop offensive AI-driven attacks. In this new era, the old security model of “trust but verify” is dead. The new model, which AI is perfect for, is Zero Trust. Zero Trust Architecture means you trust nothing and no one by default. It doesn’t matter if a login request comes from inside the office or outside; it must be verified. AI helps enforce this by continuously analyzing behavior. Just because you entered the right password doesn’t mean you are who you say you are. If your “logged-in” account suddenly starts acting suspiciously, the AI can force you to re-authenticate or block your access. Conclusion AI in Cybersecurity is a revolutionary, double-edged sword. It offers our most powerful hope for a secure digital future, capable of analyzing threats and responding at superhuman speeds. At the same time, it arms our adversaries with tools to create highly deceptive scams and intelligent malware. The key takeaway is that we can’t ignore it. For businesses, investing in modern, AI-powered defensive tools is no longer an option—it’s a necessity for survival. For individuals, it requires a new level of vigilance. In this new world, adaptability is everything. The future of security will be defined by who has the smarter, faster, and more adaptable AI. FAQ Q1: What is AI in Cybersecurity? AI in Cybersecurity refers to the use of artificial intelligence and machine learning to detect, predict, prevent, and respond to cyber threats. It moves beyond traditional, rule-based security by learning from data to identify new and unknown threats based on behavioral anomalies. Q2: Can AI replace human cybersecurity professionals? No, AI is a tool to augment human professionals, not replace them. AI can handle the massive, high-speed data analysis, but it still lacks human intuition, creativity, and strategic decision-making. AI flags the problem and contains it; the human analyst investigates the “why” and “how” to build a stronger long-term strategy. Q3: What is the biggest threat from AI in cyberattacks? Currently, the most accessible and dangerous threat is AI-powered social engineering, including deepfake audio and video. These attacks target the weakest link in any security system—human psychology—and are incredibly difficult to defend against with technology alone. Q4: How can a small business afford AI-powered security? While developing a custom AI model is expensive, most AI-powered security is now sold “as-a-service.” Many modern antivirus, firewall, and email security providers (like Microsoft, Google, and CrowdStrike) have already integrated AI and machine learning into their standard products, making it accessible and affordable for businesses of all sizes.

Scroll to Top